Eurogate Tanger listed by N0n ransomware group
Eurogate Tanger
Overview
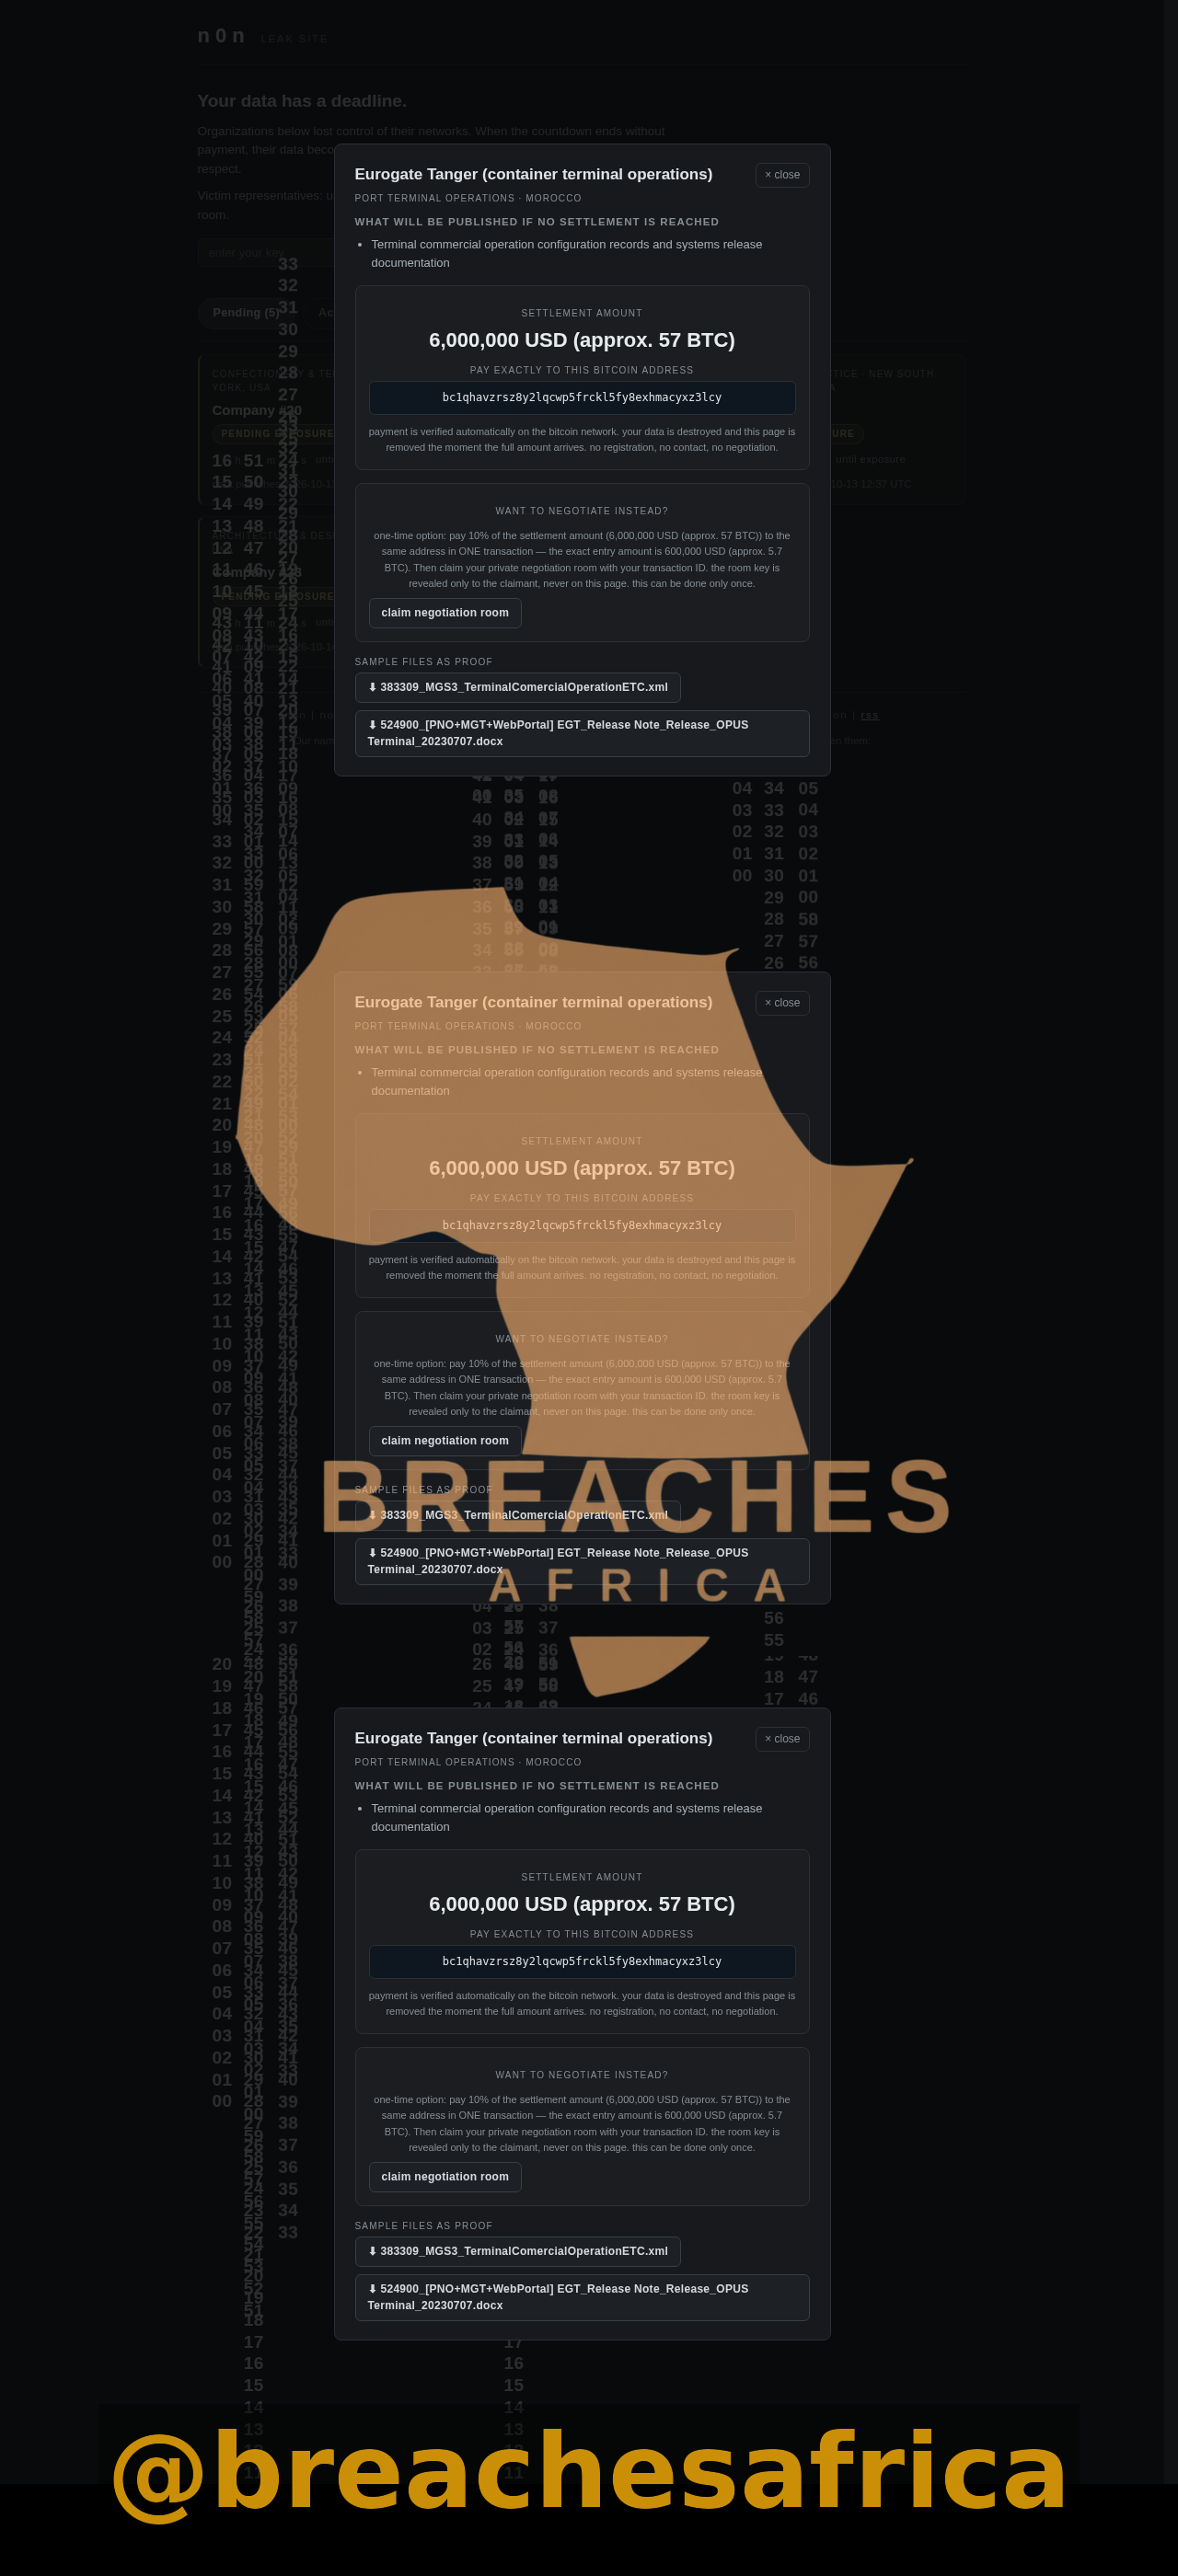
Eurogate Tanger, the operator of the container terminal at the Tanger Med port complex in Morocco, has been listed by the N0n ransomware group. The listing was published on 12 October 2026, and the group states the victim has not paid, with stolen files scheduled for release on 19 October 2026. The material described is terminal commercial operation configuration records and systems release documentation.
What was published
The group page states the following points:
- Target: container terminal operations at Tanger Med, Morocco
- Data described: commercial operation configuration records and systems release documentation
- Status: "NOT PAID", files to be published on 19 October 2026 at 13:27 UTC
- Volume of records: not disclosed in the listing
- Number of affected people: not disclosed
No archive size, file count, or sample records are visible on the public listing, and no copy of the data has been offered for free.
Risks for affected individuals
If the claim is accurate, exposed configuration and release documentation could give an attacker a map of the terminal's operational systems, including the interfaces used for commercial scheduling and cargo handling. That knowledge can support lateral movement or a follow-up intrusion, and it may expose internal contact details of staff involved in terminal operations.
The port operator itself is the primary risk holder, but downstream logistics partners, shipping lines, and customs brokers interacting with the terminal's digital workflows could also be affected if system credentials or integration details are in the material.
What remains unknown
It is not confirmed whether Eurogate Tanger has been contacted, whether a ransom demand was made, or whether the data genuinely originates from the terminal operator's systems. The size and content of the alleged leak are unverified, and no independent reporting on this specific claim has been found at the time of writing.
What affected people should do
Staff and partners of the terminal should report suspicious internal access requests to their security team. Organisations connected to the terminal's digital workflows should review credentials and integration secrets that reference Eurogate Tanger, rotate any that may have been exposed, and watch for phishing that references the incident.
Sources
- http://nongzecboljwv3yfndkggsybsglfrkffw7bvk2zemuteoxe6etpusnad.onion#v-eurogate-tanger.com