Geidea payment gateway: SQL injection claim on DarkForums covers MENA merchants and Egyptian transaction data
Geidea
Overview
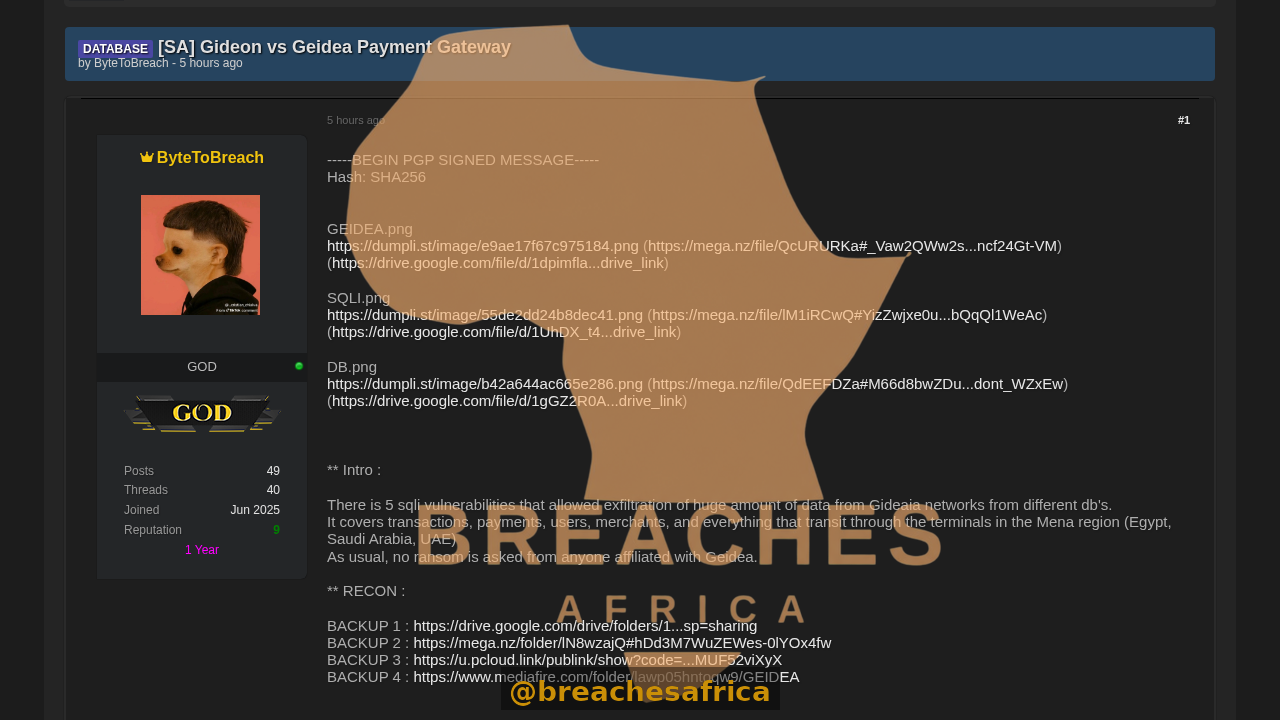
On 13 October 2026, a DarkForums member using the handle ByteToBreach published a thread titled "[SA] Gideon vs Geidea Payment Gateway". The post claims that five SQL injection vulnerabilities allowed the extraction of a large volume of data from several Geidea databases. According to the poster, the affected records cover transactions, payments, users and merchants, and the data that transits through Geidea payment terminals in the MENA region, naming Egypt, Saudi Arabia and the United Arab Emirates.
What was published
The thread does not contain an extract of the stolen data. It lists four backup mirrors hosted on Google Drive, Mega, pCloud and MediaFire, three screenshots presented as evidence of the SQL injection and of the database content, and the PGP signed message of the poster. The message states explicitly that no ransom is being demanded from any party affiliated with Geidea. The contact channels listed are Tox, Signal, Telegram and an X account.
According to the post, the exfiltrated material relates to:
- transaction and payment records processed by the gateway
- user and merchant account data
- data passing through Geidea terminals across the MENA region
No record count, no volume in gigabytes and no period covered are given for the claimed extraction. The poster account ByteToBreach shows a GOD rank on the forum, 49 posts and 40 threads created, and a registration date of June 2025. The account is not flagged as banned.
Risks for affected individuals
- Exposed payment data can support fraudulent transactions and unauthorised charges.
- Merchant account data may be reused for invoice fraud and business email compromise.
- Identity and contact data can feed phishing and account takeover attempts against consumers and merchants.
- The public contact handles listed in the post create a direct channel for follow-up extortion attempts.
What remains unknown
The volume of the claimed extraction, the exact databases affected and the period covered are not stated. No sample extract was published in the thread itself. Geidea has not issued a public statement on the claim, and no independent confirmation was found in open sources, so the breach remains a forum claim. The identity behind the ByteToBreach handle is not established.
What affected people should do
Merchants using Geidea terminals or the online gateway should review recent settlement and transaction records and request a status update from Geidea. Consumers should check card statements for unfamiliar charges and enable transaction alerts. Because the post lists public mirrors and social handles, messages referencing this incident should be treated as unconfirmed until the company states otherwise.
Sources
- https://darkforums.as/Thread-DATABASE-SA-Gideon-vs-Geidea-Payment-Gateway