SANAtech Global Solutions listed by the UmBra ransomware group
SANAtech Global Solutions
Overview
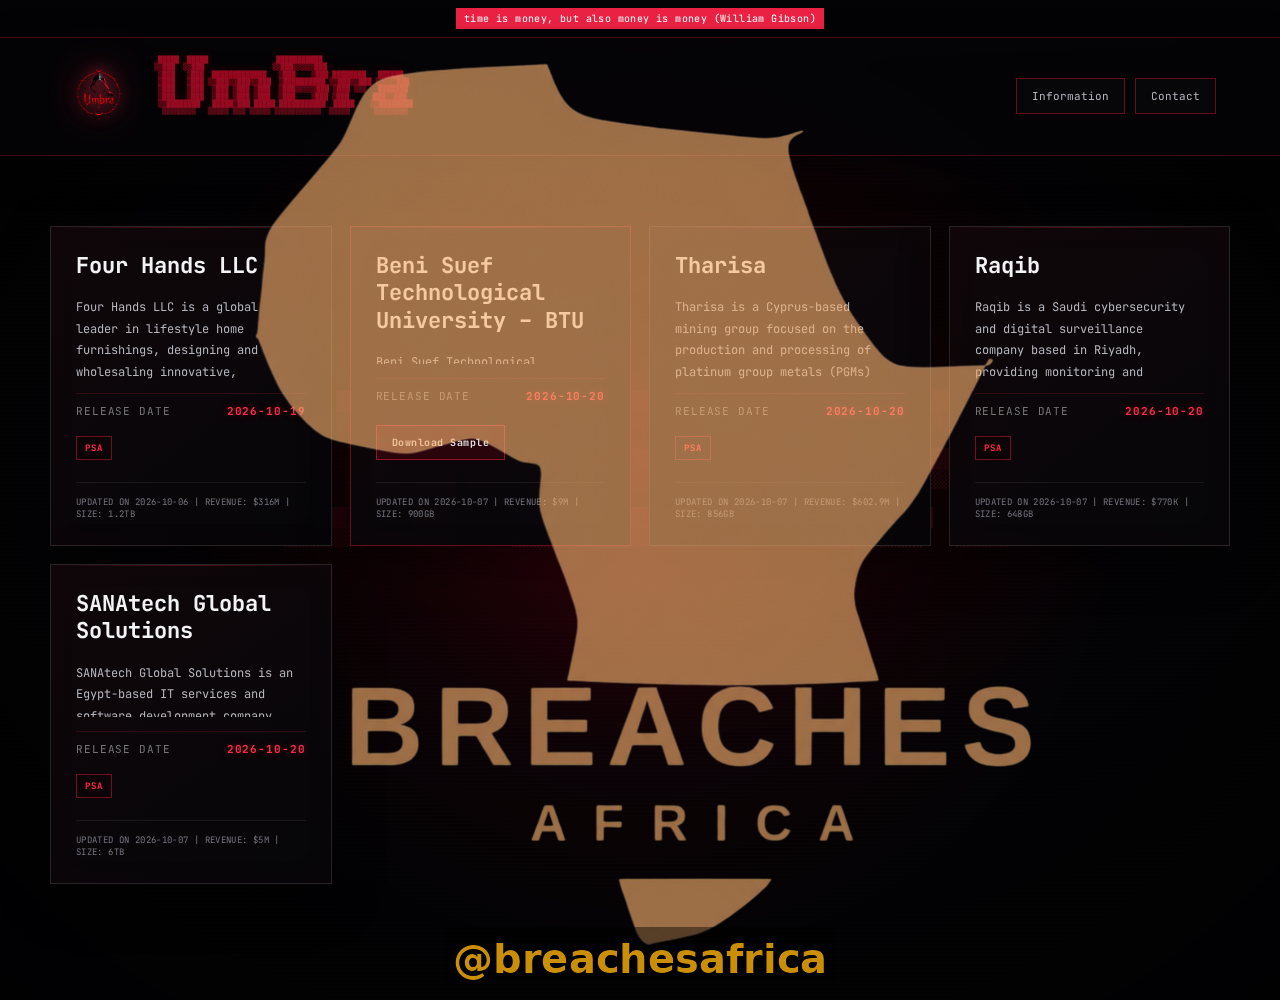
On 7 October 2026, the UmBra ransomware group added SANAtech Global Solutions to its Tor-based leak site. SANAtech is an Egypt-based IT services and software development company headquartered in Cairo, serving clients in Egypt, the United States and Canada. The entry carries no data volume, no ransom figure and no published sample files.
What was published
The leak-site entry is a victim profile rather than a data dump. It contains the following elements and nothing more:
- Claimed victim: SANAtech Global Solutions
- Domain named:
sanatechgs.com - Location stated: Cairo, Egypt
- Group: UmBra
- Listing date: 7 October 2026, 11:26 UTC
- Sector tag:
Technology - Data volume: not disclosed
- Ransom demand: not disclosed
- Evidence attached: none beyond the profile page
UmBra has kept this layout across its recent activity: a profile, a sector tag and a Tor-hosted page, with no archive, file tree or record count. Our team has not seen a sample of the claimed data.
Actor statement and external coverage
Coverage published the same day by DeXpose reports a group statement attached to the claim: "The full leak will be published soon, unless a company representative contacts us via the channels provided." The wording matches the UmBra pattern of using a public listing as leverage before negotiation. Because no sample has appeared, the size and content of the alleged dataset remain claims by the actor and are not independently verified.
Position within UmBra recent activity
SANAtech sits inside a cluster of Egyptian targets that UmBra published in the first half of October 2026, alongside the Faculty of Specific Education at Cairo University, Helwan International Technological University (HITU) and Beni Suef Technological University (BTU).
Risks if the claim is confirmed
- A services company may hold access paths, credentials or documentation belonging to its clients, so exposure could reach beyond the company itself.
- Staff records, project documentation and client contracts are the usual material in service-provider exfiltration.
What remains unknown
- Whether UmBra holds any SANAtech data at all, and if so its volume, categories and age.
- Whether a ransom has been demanded or paid, and whether any negotiation is under way.
- Whether SANAtech has engaged incident response or notified Egyptian authorities.
What affected people should do
Treat any unsolicited message that quotes internal SANAtech details as a phishing attempt and report it. Staff should change company account passwords and enable multi-factor authentication. Clients should ask the firm for a written status update and treat shared credentials as exposed until SANAtech confirms otherwise.
Sources
- https://www.ransomware.live/id/U0FOQXRlY2ggR2xvYmFsIFNvbHV0aW9uc0BVbUJyYQ
- https://www.dexpose.io/umbra-ransomware-targets-sanatech-global-solutions/
- http://umbra7isogjsgdcndz3uu6qvl5zftjptt6s3iiuecjlwbt4yqyvrhcid.onion