Tharisa: Breach Report
Tharisa
Overview
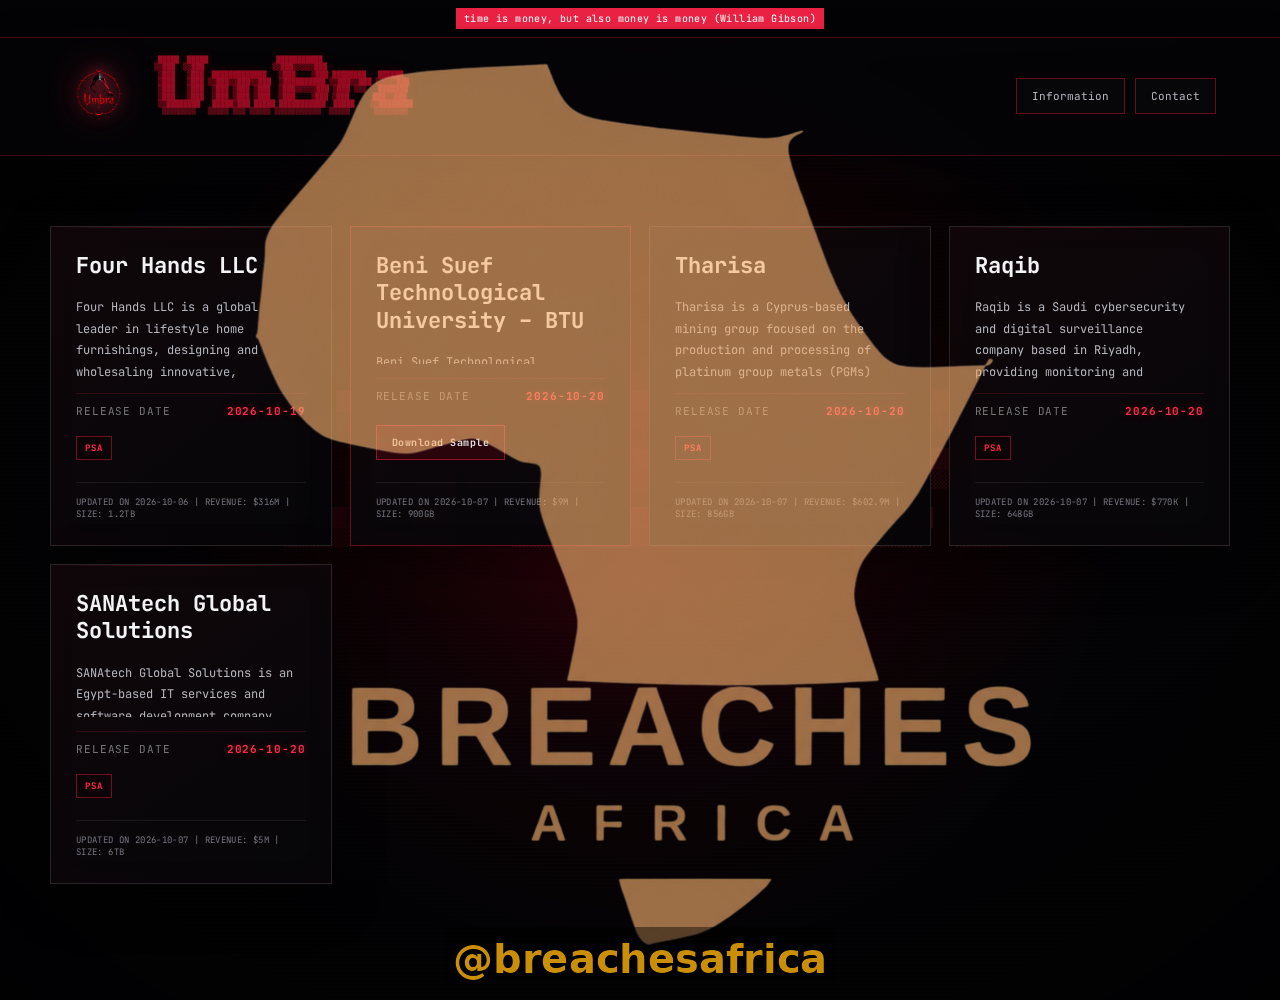
The UmBra ransomware group has added Tharisa, a Cyprus-incorporated mining group operating in South Africa and Zimbabwe, to its dark web leak blog. The listing appeared on 7 October 2026 and profiles the production and processing of platinum group metals (PGMs) and chrome as the target profile.
What was published
The post did not disclose a data volume or a deadline by the time of capture. UmBra's listing typically names a victim and later releases sample data or a full archive if no payment is made. No specific files, record counts, or compromise date were listed for Tharisa.
- Victim sector: mining and metals processing (PGMs and chrome)
- Operations: South Africa and development projects in Zimbabwe
- Claimed actor: UmBra
- Disclosed volume: not disclosed
Risks for affected individuals
As a business-to-business disclosure, the immediate risk affects Tharisa's operations, supply chain, and commercial counterparties located mainly in South Africa and Zimbabwe. Financial details, project documents, or staff records, if later released, would affect trust and compliance with regional data protection rules.
What remains unknown
- The amount and type of data exfiltrated, if any
- Whether the claim is a negotiation tactic or a confirmed intrusion
- The attack vector and the timeline between compromise and listing
- Any response or payment status from Tharisa
What affected people should do
Staff, suppliers, and partners should review any correspondence sent to them in recent weeks for signs of manipulation. Tharisa and its counterparties should monitor dark web mentions, preserve logs, and follow the guidance of their incident response teams. The organisation should notify regulators if confirmed records are exposed.